THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

Canary Trap
Fortifying Digital Fortresses with Expert Security Testing and Advisory Services
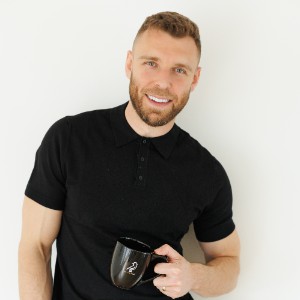 Daniel Pizon, President and CEO
In 2023, the Securities and Exchange Commission (SEC) released its 'Rules on Cybersecurity Risk Management, Strategy, Governance and Incident Disclosure' for publicly traded companies. With federal, state, and provincial regulations now in place and enforced, cybersecurity is increasingly prioritized as a strategic imperative by nearly every board and senior leadership team. Significant investments in people, processes, and technology are becoming commonplace, often focusing on implementing defensive and reactive measures. However, to effectively address the cybersecurity challenge, organizations must adopt a proactive approach. Proactivity enables organizations to stay ahead of evolving threats and safeguard digital assets and sensitive data.
Canary Trap is a laser-focused, boutique offensive security services and advisory firm that specializes in delivering true adversarial offensive security (penetration) testing.
"Our elite team of security experts can be contracted to test the security resiliency of your most critical digital assets and networks. We will identify, enumerate, and report on security gaps and vulnerabilities prone to exploitation by sophisticated cybercriminals," says Daniel Pizon, president and CEO of Canary Trap. "Undertaking regular penetration testing and related security assessments has long been established as a best practice."
Employing more than thirty (30) highly skilled, credentialed, and certified security experts, Canary Trap specializes in conducting penetration testing against external and internal networks, web and mobile applications, APIs, and wireless security assessments. Additionally, Canary Trap offers assessment and advisory services, including Microsoft 365 security controls reviews, cloud configuration reviews, physical security assessments, and cybersecurity incident management planning. These services uncover unknown vulnerabilities, gaps, and weaknesses that could be exploited.
Canary Trap continuously refines and enhances its processes and methodologies that underpin service delivery. This is achieved through strategic investments in new technologies, capabilities, and, most importantly, its employees. All Canary Trap employees are allocated a significant annual training budget to upskill and keep pace with the ever-changing threat landscape. At the conclusion of each engagement, Canary Trap delivers a Report of Findings that showcases the results of testing, along with any identified security gaps prioritized by risk and impact. The company conducts a robust Quality Assurance (QA) process to ensure accuracy.
Offering competitive pricing without compromise has earned Canary Trap a growing and loyal client base. In 2024, Canary Trap anticipates undertaking no fewer than five hundred (500) unique engagements. The company works closely with organizations across diverse industries, including aerospace, utilities, manufacturers, healthcare, retail, and financial institutions. Additionally, it maintains significant lines of business within the public sector, such as municipalities, state, and provincial government agencies.
Canary Trap's rapid growth has attracted the attention of industry analysts. The company has been featured in numerous publications, including CIOReview, BizTech Outlook, GRC Outlook, CIO Bulletin, and our own Enterprise Security Magazine. We asked Daniel to provide a relevant example that highlights Canary Trap’s leadership position within the offensive security services marketplace.
In 2022, Canary Trap was approached by a large enterprise client—a well-known financial institution with an established reputation for its sophisticated cybersecurity program. The client typically worked exclusively with large consulting firms on all cybersecurity matters. A critical web application was nearing general availability (GA) and had been cleared by their previous testing firms. Seeking a fresh perspective to challenge their defences, the organization turned to Canary Trap.
Canary Trap got to work, meticulously combing through layers of security, code, and infrastructure. Days turned into nights, and nights into days, as the company employed a variety of tactics from social engineering to advanced cryptanalysis. It was during a late-night session, fuelled by pizza and determination, that one of Canary Trap’s SMEs stumbled upon an anomaly.
Hidden deep within the bank's network were a series of irregularities that hinted at a possible backdoor. As the team investigated further, they unravelled a complex web of misconfigurations and overlooked security patches in the supporting infrastructure that led to a CRITICAL vulnerability. It was a zero-day exploit—a treasure trove for any hacker—and it had gone unnoticed by all who had come before.
The vulnerability lay at the very heart of the enterprise’s operations, within a subsystem deemed impenetrable. It stands as a testament to Canary Trap’s tenacity and skill that they identified what others had missed. The discovery was not just a technical triumph but also a narrative of David versus Goliath, where the smaller, more agile firm outsmarted the giants of the industry.
Canary Trap presented its findings to the client, who was initially skeptical yet grateful. The vulnerability was swiftly patched, and Canary Trap was awarded a multiyear contract that continues to this day. This example serves as a reminder that in the world of cybersecurity, it’s not always the biggest that prevails, but the sharpest and most persistent.
Our security analysts and ethical hackers work closely with clients to test the resiliency of their cyber environment, identifying and reporting on security gaps and vulnerabilities that are prone to exploitation

The presence of skilled and inquisitive cybersecurity testers with certifications such as International Information System Security Certification Consortium (ISC2), Certified Information Security Manager (CISM), OffSec Certified Professional (OSCP), Certified Information Systems Security Professional (CISSP), and Certified Ethical Hacker (CEH) enables the strategic allocation of resources to specific projects. Canary Trap provides staff with continuous training and access to top-of-the-line commercial tools. It also seeks to hire security practitioners with diverse backgrounds, experiences, and skill sets to take a holistic approach.
Canary Trap has a demonstrated track record of making continuous improvements over time. The company has built a strong reputation as the definitive leader in offensive security testing and advisory services, consistently outperforming global behemoths. With a proven history of delivering results and value for money, Canary Trap has earned a respected name within the competitive world of cybersecurity. If you’re seeking to enhance your organization's resilience against sophisticated attacks, Canary Trap is here to help.
Company
Canary Trap
Management
Daniel Pizon, President and CEO
Description
Canary Trap is a laser-focused, boutique cyber-security services company that assists clients in identifying and responding to security gaps before becoming the next victim of a breach. It combines human expertise with sophisticated tools and threat intelligence to ensure a thorough, in-depth approach to all security testing and assessments.